Data Protection Schedule
Introduction
Forcefield is a trading name of The Keyholding Company Limited, incorporated and registered in England and Wales with company number 03538605, whose registered office is at 28 Kirby Street, London, EC1N 8TE (Forcefield).
Definitions
Applicable Laws:
a) To the extent the UK GDPR applies, the law of the United Kingdom or of a part of the United Kingdom.
b) To the extent EU GDPR applies, the law of the European Union or any member state of the European Union to which Forcefield is subject.
Applicable Data Protection Laws:
a) To the extent the UK GDPR applies, the law of the United Kingdom or of a part of the United Kingdom which relates to the protection of personal data.
b) To the extent the EU GDPR applies, the law of the European Union or any member state of the European Union to which Forcefield is subject, which relates to the protection of personal data.
Client Personal Data: any personal data which Forcefield processes in connection with this agreement, in the capacity of a processor on behalf of the Client.
EU GDPR: the General Data Protection Regulation ((EU) 2016/679).
Forcefield Personal Data: any personal data which Forcefield processes in connection with this agreement, in the capacity of a controller.
Purpose: the purposes for which the Client Personal Data is processed, as set out in Annex B.
UK GDPR: has the meaning given to it in the Data Protection Act 2018.
1. Data Protection
1.1 For the purposes of this clause 1, the terms controller, processor, data subject, personal data, personal data breach and processing shall have the meaning given to them in the UK GDPR.
1.2 Both parties will comply with all applicable requirements of Applicable Data Protection Laws. This clause 1 is in addition to, and does not relieve, remove or replace, a party’s obligations or rights under Applicable Data Protection Laws.
1.3 The parties have determined that, for the purposes of Applicable Data Protection Laws:
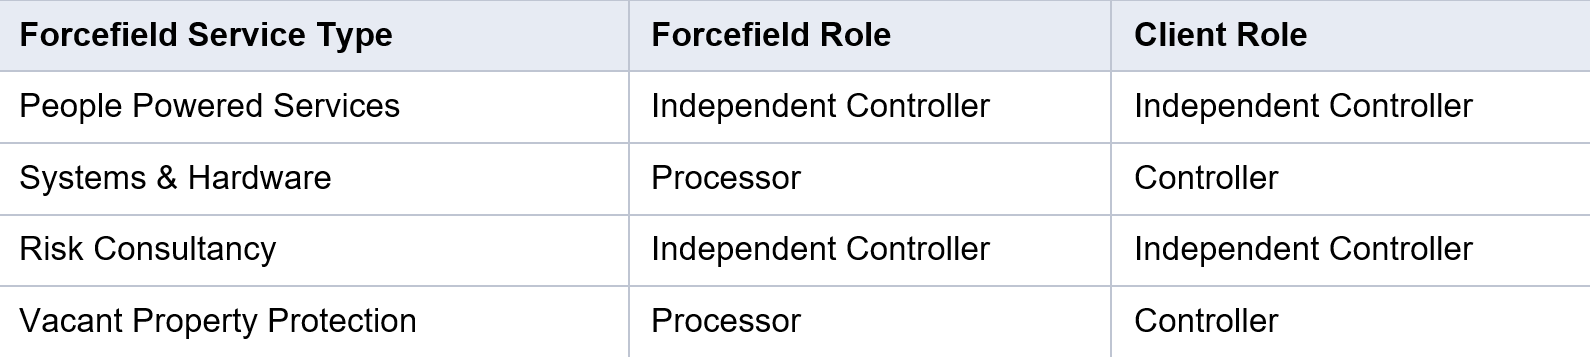
(a) Forcefield shall act as an independent controller in respect of the personal data and processing activities identified in Annex A; and
(b) Forcefield shall process the personal data, as a processor on behalf of the Client in respect of the processing activities identified in Annex A.
1.4 Should the determination in clause 1.3 change, then each party shall work together in good faith to make any changes which are necessary to this clause 1 or the related Annexes.
1.5 Without prejudice to the generality of clause 1.2, the Client will ensure that it has all necessary appropriate consents and notices in place to enable lawful transfer of Forcefield Personal Data and Client Personal Data to Forcefield and/or lawful collection of the same by Forcefield for the duration and purposes of this agreement.
1.6 In relation to the Client Personal Data, Annex B sets out the scope, nature and purpose of processing by Forcefield, the duration of the processing and the types of personal data and categories of data subject.
1.7 Without prejudice to the generality of clause 1.2 Forcefield shall, in relation to Client Personal Data:
(a) process that Client Personal Data only on the documented instructions of the Client, which shall be to process the Client Personal Data for the purposes set out in Annex B, unless Forcefield is required by Applicable Laws to otherwise process that Client Personal Data. Where Forcefield is relying on Applicable Laws as the basis for processing Client Personal Data, Forcefield shall notify the Client of this before performing the processing required by the Applicable Laws unless those Applicable Laws prohibit Forcefield from so notifying the Client on important grounds of public interest. Forcefield shall inform the Client if, in the opinion of Forcefield, the instructions of the Client infringe Applicable Data Protection Laws;
(b) implement the technical and organisational measures set out in Annex C to protect against unauthorised or unlawful processing of Client Personal Data and against accidental loss or destruction of, or damage to, Client Personal Data, which the Client has reviewed and confirms are appropriate to the harm that might result from the unauthorised or unlawful processing or accidental loss, destruction or damage and the nature of the data to be protected, having regard to the state of technological development and the cost of implementing any measures;
(c) ensure that any personnel engaged and authorised by Forcefield to process Client Personal Data have committed themselves to confidentiality or are under an appropriate statutory or common law obligation of confidentiality;
(d) assist the Client insofar as this is possible (taking into account the nature of the processing and the information available to Forcefield), and at the Client’s cost and written request, in responding to any request from a data subject and in ensuring the Client’s compliance with its obligations under Applicable Data Protection Laws with respect to security, breach notifications, impact assessments and consultations with supervisory authorities or regulators;
(e) notify the Client without undue delay on becoming aware of a personal data breach involving the Client Personal Data;
(f) at the written direction of the Client, delete or return Client Personal Data and copies thereof to the Client on termination of the agreement unless Forcefield is required by Applicable Laws to continue to process that Client Personal Data. For the purposes of this clause 1.7(f) Client Personal Data shall be considered deleted where it is put beyond further use by Forcefield; and
(g) maintain records to demonstrate its compliance with this clause 1.7.
1.8 The Client hereby provides its prior, general authorisation for Forcefield to:
(a) appoint processors to process the Client Personal Data, provided that Forcefield:
(i) shall ensure that the terms on which it appoints such processors comply with Applicable Data Protection Laws, and are consistent with the obligations imposed on Forcefield in this clause 1;
(ii) shall remain responsible for the acts and omission of any such processor as if they were the acts and omissions of Forcefield; and
(iii) shall inform the Client of any intended changes concerning the addition or replacement of the processors, thereby giving the Client the opportunity to object to such changes provided that if the Client objects to the changes and cannot demonstrate, to Forcefield’s reasonable satisfaction, that the objection is due to an actual or likely breach of Applicable Data Protection Laws, the Client shall indemnify Forcefield for any losses, damages, costs (including legal fees) and expenses suffered by Forcefield in accommodating the objection.
(b) transfer Client Personal Data outside of the UK as required for the Purpose, provided that Forcefield shall ensure that all such transfers are effected in accordance with Applicable Data Protection Laws. For these purposes, the Client shall promptly comply with any reasonable request of Forcefield, including any request to enter into standard data protection clauses adopted by the EU Commission from time to time (where the EU GDPR applies to the transfer) or adopted by the UK Information Commissioner from time to time (where the UK GDPR applies to the transfer).
1.9 Controller Obligations
(a) Acknowledgement of Roles. The parties acknowledge in respect of the receipt of certain services where Forcefield is identified as a controller, each party will be an independent controller with respect to the personal data that it processes. Each party shall individually determine the purposes and means of its processing of personal data.
(b) Mutual Compliance Obligation. Each party shall be individually responsible for its compliance with all Applicable Data Protection Laws. Each party shall maintain all necessary records of processing activities and shall be responsible for its own interactions with supervisory authorities.
(c) Data Subject Rights & Transparency. Each party is solely responsible for providing its own privacy notices to data subjects (data subjects include employees, customers, or end-users) as required by Applicable Data Protection Laws. Furthermore, each party shall be responsible for handling requests from data subjects seeking to exercise their rights (e.g., access, deletion) in relation to the personal data under its control.
(d) Data Breach Notification and Cooperation. If a personal data breach occurs that is likely to affect the shared personal data, the party experiencing the breach shall promptly notify the other party without undue delay. The notifying party will provide sufficient information to enable the non-breaching party to meet its own obligations under Applicable Data Protection Laws, including notifying regulators or affected individuals if necessary.
(e) Security Measures. Each party shall implement and maintain appropriate technical and organisational measures to ensure a level of security appropriate to the risk to protect the shared personal data from unauthorised or unlawful processing and against accidental loss, destruction, or damage.
Annex A: Role of the Parties
Annex B: Particulars of the Processing
Particulars of processing: Collection, storage, transmission, access, retrieval, reporting, deletion.
Scope: The provision of the Services.
Nature: Delivery of security response, and operational services in person and via systems.
Purpose of processing: The provision of the Services.
Duration of the processing: Term of the relevant client contract.
Types of Personal Data: Names, contact details, access logs, incident reports, CCTV images, alarm records, geolocation, timestamps, photo, ID numbers, vehicle registration plate, security footage, access control movements, uniform sizes, pay; email addresses, bank account information.
Categories of Data Subject: Forcefield employees; Forcefield Clients; Client employees; customers of the Clients, employees of Service Partners.
Annex C: Technical & Organisational Measures
Taking into account the state of the art, the costs of implementation and the nature, scope, context and purposes of processing as well as the risks to data subjects, Forcefield shall implement appropriate technical and organisational measures to ensure a level of security appropriate to the risk. Forcefield shall implement the following, as appropriate:
(a) the pseudonymisation and encryption of the Client Personal Data;
(b) the ability to ensure the ongoing confidentiality, integrity, availability and resilience of processing systems and services;
(c) the ability to restore the availability and access to Client Personal Data in a timely manner in the event of a physical or technical incident; and
(d) a process for regularly testing, assessing and evaluating the effectiveness of technical and organisational measures for ensuring the security of the processing.
In assessing the appropriate level of security account shall be taken in particular of the risks that are presented by processing, in particular from accidental or unlawful destruction, loss, alteration, unauthorised disclosure of, or access to Client Personal Data transmitted, stored or otherwise processed.
As a minimum, Forcefield shall implement the items set out below:
Organisational Measures
Forcefield shall implement the following policies:
- Data Protection Policy
- Information Security Policy
- Data Subjects’ Rights Procedure
- Personal Data Breach Procedure
- Equipment Policy
- Clear Desk and Clear Screen Policy
- Information Classification Policy
- Acceptable Use Policy
- Password Management Policy
- Business Continuity Policy
- User Access Control Policy
- Backup and Restore Policy
- Cryptographic Control Policy
Forcefield shall ensure that all personnel that process and/or have access to Client Personal Data have data protection awareness training upon induction and regular refresher training thereafter.
Technical Measures
Forcefield shall implement the following measures, as appropriate:
- Firewalls
- Anti-malware
- Encryption of personal data
- Access controls
- Penetration testing
- Vulnerability scanning
- Threat Detection
- Multifactor Authentication
- Monitoring and Logging
- Ransomware Protection
- Email monitoring